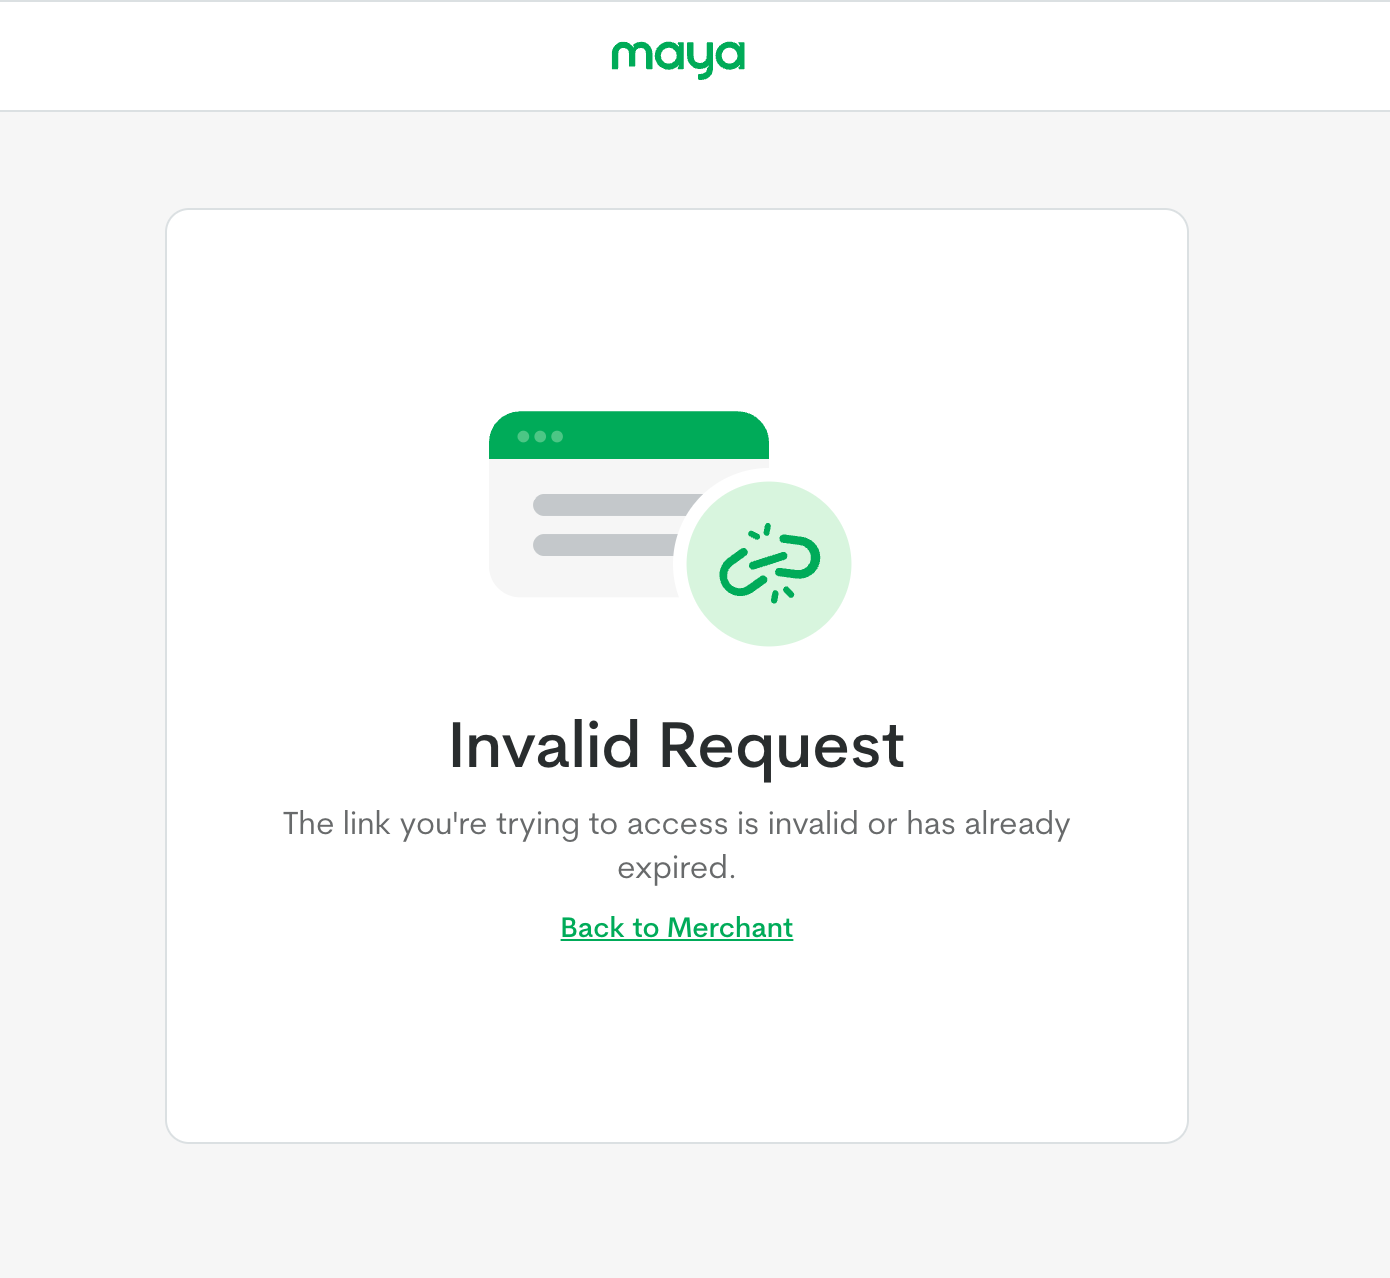
I am currently integrating the Maya Checkout API (/checkout/v1/checkouts) into my application. Everything works perfectly in the Sandbox environment when using a Card payment, but I am consistently hitting an error when testing the Maya Wallet payment flow.
The Issue:
I generate the checkout session successfully and receive the checkoutId and redirect URL.
I open the checkout link, select “Maya Wallet”, and log in using the official sandbox test credentials( 09900100900 ).
The checkout screen successfully loads the transaction details.
The moment I click “Confirm to Pay”, the page shows “Invalid Request” screen (The link you’re trying to access is invalid or has already expired)
It seems you may be referring to the sandbox Maya Wallet username as ‘09900100900’, but the correct format is ‘+639900100900’. The country code ‘+63’ is required and must be included exactly as specified in the documentation. When testing Maya Wallet payments in Sandbox, use the following credentials:
Username: +639900100900
Password: Password@1
OTP: 123456
Using an incorrectly formatted username (e.g., missing ‘+63’) will cause the authentication session to be invalidated, resulting in the ‘Invalid Request’ error upon confirmation. Ensure you are using the full, correctly formatted phone number including ‘+63’ when logging in. This is the most likely cause of your issue.
For Sandbox concerns and other technical implementation inquiries, please get in touch with us via:
Sandbox Health Page: Check real-time service status updates.
Maya Developer Hub Service Desk: File
a ticket in Sandbox.
To Know More:
We value your input and would love to hear your insights. Please submit you feedback here.
I have already tested using the exact +639900100900 format (along with the correct OTP/PIN from the docs) and the exact same error occurs.
To clarify, authentication is not the issue. 1. The login is successful. 2. The OTP verification is successful. 3. The checkout screen successfully loads the transaction details.
The “Invalid Request” only happens at the very end after tapping the final “Confirm to Pay” button.
Hi @frances.kagahastian, just checking in on this! Are there any updates from the engineering team? The sandbox wallet is still dropping the session with the ‘Invalid Request’ error as of today. Really appreciate your help with this!
I experienced a similar cross-domain session drop when working with dynamic redirect URLs in external sandbox environments. In my case, the root cause was related to strict SameSite cookie policies and CORS settings blocking session token propagation across domain boundaries during the checkout confirmation phase.
To fix it, double-check your callback handling:
Cookie Attributes: Ensure your session/auth cookies explicitly specify SameSite=None and Secure so they survive cross-origin redirects from external gateways.
Dynamic Return URLs: Explicitly pass fully qualified return/cancel URLs with necessary session identifiers in the payload rather than relying on browser session persistence across redirects.
CORS Headers: Ensure your server allows cross-domain credentials (Access-Control-Allow-Credentials: true) for the domain making the post-payment callback.
If anyone is looking to Find a sideline project or explore practical solutions for integration issues like this, testing with explicit callback parameters usually resolves the invalid request error during checkout confirmation.